Create custom roles and grant direct permissions
The built-in roles do not fit, or someone needs access to exactly one scene, playlist, or a single display.
- For
- Owners who tailor permissions
- Prerequisite
- the Owner role and the Pro package
- Where in the portal
- Settings › Organization › Roles › Create role. You grant direct permissions under Settings › Organization › Team: open an entry, then the Direct permissions (grants) card.
On this page
If the three built-in roles don’t fit, create a role of your own with exactly the permissions you need. For a single scene, playlist, or display, you can also grant or deny one person access directly.
Steps
Read the comparison matrix
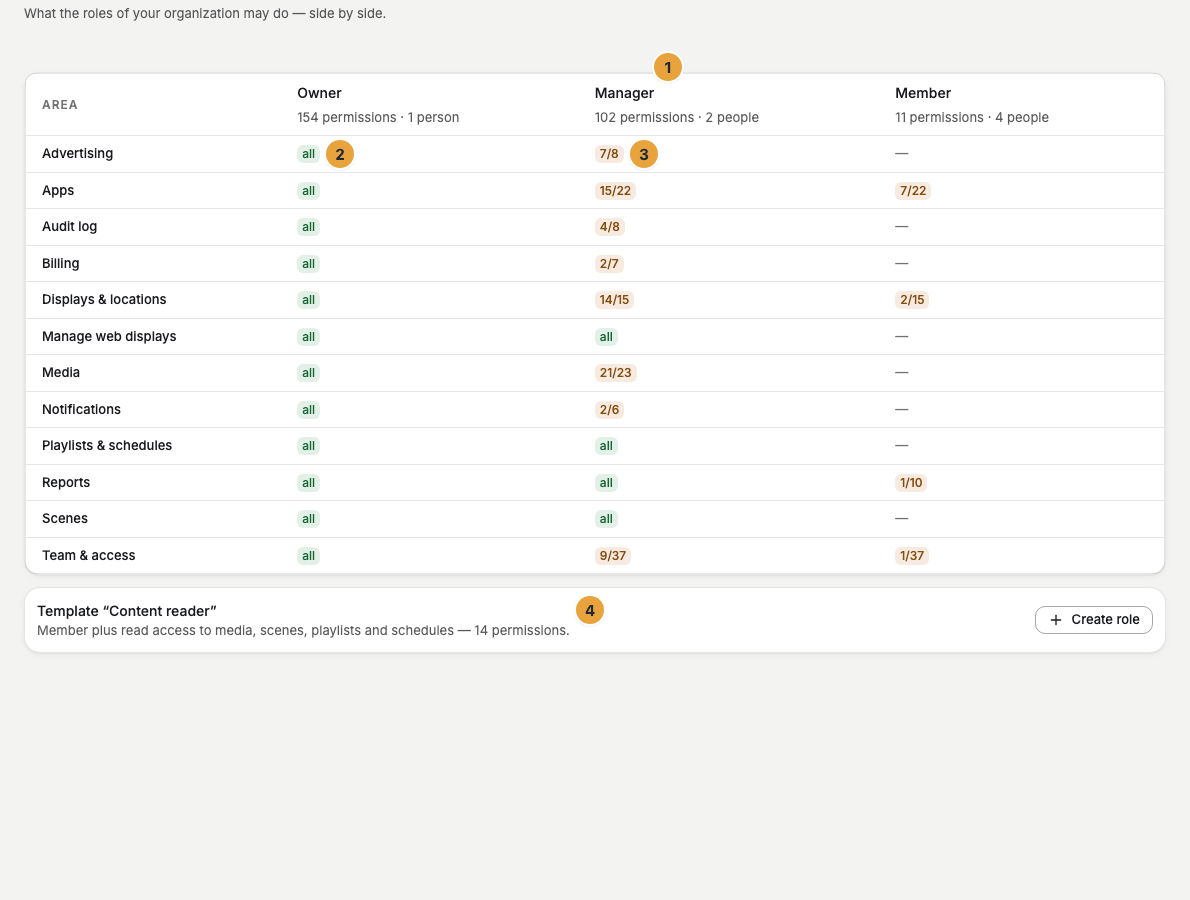
The Roles tab shows a comparison matrix: the roles as columns and the areas of permissions (column Area) as rows. Each cell says all, gives a fraction such as “2/7” (on hover “2 of 7 permissions”), or shows a dash. The column header shows the number of permissions and the number of people with this role, such as “12 permissions · 4 people”. A role you are not allowed to assign shows Not grantable there, along with the reason: “contains 2 permissions you do not hold” or “only an owner can assign this role.”
In the Starter package, the tab shows Read-only.: “Managing roles starts with Pro.”
Create a custom role
- Click Create role. The dialog New role (“Create a custom role. Assign permissions afterwards in the editor.”) asks for Name and Description.
- Open the new role from its column header. The editor has two sections: Details for name and description, and Permissions for the permission set: “Expand a resource group and select the permissions.”
- Select the permissions. The picker shows the permission catalog of your organization with a plain-language description for each permission. What you do not hold yourself stays visible but is disabled: “You can only grant permissions you hold yourself.”
- Click Save. Role saved appears.
For the most common case, one click is enough: Below the matrix is the Template “Content reader” — Member plus read access to media, scenes, playlists and schedules. The template disappears as soon as the role exists.
Delete a role
To delete a custom role, use the menu in the column header or Delete role in the editor. Confirm the Delete role? prompt with Delete permanently. This works only as long as nobody holds the role anymore. If someone still holds it, the entry is disabled: “Still held by 3 people — assign a different role first.” If the role is set as the default role of a company sign-in, the note asks you to set a different one there first. Built-in roles have no menu. They are read-only.
If someone saved the role at the same time, the portal asks The role changed in the meantime and lets you choose between Keep draft and Load the other version. Nothing is silently overwritten.
Grant or revoke a direct permission
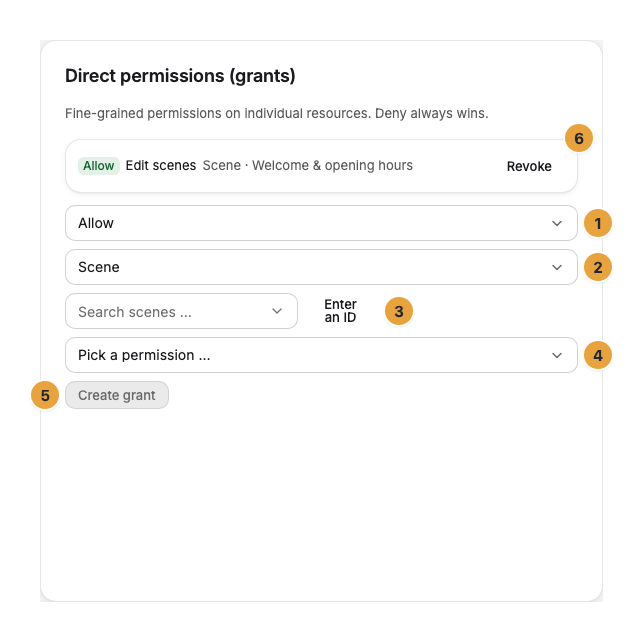
Open the person’s entry and go to the Direct permissions (grants) card: “Fine-grained permissions on individual resources. Deny always wins.”
- Choose the kind: Allow or Deny.
- Choose the resource type (Scene, Playlist, Schedule, Display, or Media item) and the object within it. With Enter an ID, you enter it directly (such as
scn_…). With Pick from list, you search for it. - Under Pick a permission …, choose the relevant permission and click Create grant.
To remove an existing direct permission, click Revoke. A Deny always wins: no role and no second allow can override it.
Check the result
- The new role appears as its own column in the matrix, with its permission count and, at first, no one holding it.
- After you create a direct permission, Grant created appears, and after you remove one, Grant revoked.
- Both appear in the Settings › Organization › Change log with your name.
If something goes wrong
| Symptom | Cause | Solution |
|---|---|---|
| A permission stays disabled in the picker | You do not hold it yourself | “You can only grant permissions you hold yourself.” Ask a person with a wider scope. |
| A member cannot edit scenes or media | The normal case: Member is read-only | Give a direct permission or assign a custom role. |
| Someone keeps a permission despite a changed role | An Allow works in addition to the role | Revoke the direct permission. |
| Someone is not allowed to do something although the role allows it | A Deny beats the role | Revoke the denying direct permission. |
| The picker list of a resource type stays empty | “You lack the list permission for this type — the picker would stay empty.” | Enter the ID directly or have the list permission granted to you. |
Related
Was this helpful?